Security Magazine logo
search
cart
facebook twitter linkedin youtube
  • Sign In
  • Create Account
  • Sign Out
  • My Account
Security Magazine logo
  • NEWS
    • Security Newswire
    • Technologies & Solutions
  • MANAGEMENT
    • Leadership Management
    • Enterprise Services
    • Security Education & Training
    • Logical Security
    • Security & Business Resilience
    • Profiles in Excellence
  • PHYSICAL
    • Access Management
    • Fire & Life Safety
    • Identity Management
    • Physical Security
    • Video Surveillance
    • Case Studies (Physical)
  • CYBER
    • Cybersecurity News
    • More
  • BLOG
  • COLUMNS
    • Career Intelligence
    • Cyber Tactics
    • Cybersecurity Education & Training
    • Leadership & Management
    • Security Talk
  • EXCLUSIVES
    • Annual Guarding Report
    • Most Influential People in Security
    • The Security Benchmark Report
    • Top Guard and Security Officer Companies
    • Top Cybersecurity Leaders
    • Women in Security
  • SECTORS
    • Arenas / Stadiums / Leagues / Entertainment
    • Banking/Finance/Insurance
    • Construction, Real Estate, Property Management
    • Education: K-12
    • Education: University
    • Government: Federal, State and Local
    • Hospitality & Casinos
    • Hospitals & Medical Centers
    • Infrastructure:Electric,Gas & Water
    • Ports: Sea, Land, & Air
    • Retail/Restaurants/Convenience
    • Transportation/Logistics/Supply Chain/Distribution/ Warehousing
  • EVENTS
    • Industry Events
    • Webinars
    • Solutions by Sector
    • Security 500 Conference
  • MEDIA
    • Interactive Spotlight
    • Photo Galleries
    • Podcasts
    • Polls
    • Videos
      • Cybersecurity & Geopolitical Discussion
      • Ask Me Anything (AMA) Series
  • MORE
    • Call for Entries
    • Classifieds & Job Listings
    • Newsletter
    • Sponsor Insights
    • Store
    • White Papers
  • EMAG
    • eMagazine
    • This Month's Content
    • Advertise
  • SIGN UP!
CybersecuritySecurity NewswireCybersecurity News

GAO: Federal Agencies Need to Coordinate on Requirements and Assessments of States
keys-cyber-enews
May 28, 2020

Although the Centers for Medicare and Medicaid Services (CMS), Federal Bureau of Investigation (FBI), Internal Revenue Service (IRS), and Social Security Administration (SSA) each established requirements to secure data that states receive, these requirements often had conflicting parameters, says the U.S. Government Accountability Office (GAO) in a new report. 

According to GAO, such parameters involve agencies defining specific values like the number of consecutive unsuccessful logon attempts prior to locking out the user. Among the four federal agencies, the percentage of total requirements with conflicting parameters ranged from 49 percent to 79 percent, GAO found.

Regarding variance with National Institute of Standards and Technology guidance, GAO found that the extent to which the four agencies did not fully address guidance varied from 9 percent to 53 percent of total requirements. The variances were due in part to the federal agencies' insufficient coordination in establishing requirements, says GAO.

Although the Office of Management and Budget's (OMB) Circular A-130 requires agencies to coordinate, OMB has not ensured that agencies have done so. Further, while federal agencies' variance among requirements may be justified in some cases because of particular agency mission needs, the resulting impact on states is significant, according to state chief information security officers (see figure).
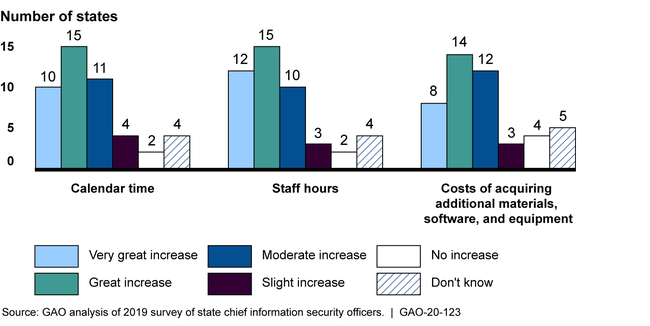
GAO

The four federal agencies that GAO reviewed either fully or partially had policies for coordinating assessments with states, but none of them had policies for coordinating assessments with each other. State chief information security officers that GAO surveyed reinforced the need to coordinate assessments by identifying impacts on state agencies' costs, including multiple federal agencies that requested the same documentation.

Coordinating with state and federal agencies when assessing state agencies' cybersecurity may help to minimize states' cost and time impacts and reduce associated federal costs, notes the report. Federal agencies reported spending about $45 million for fiscal years 2016 through 2018 on assessments of state agencies' cybersecurity, says GAO. 

Recommendations for Executive Action

  1. Recommendation: The Director of OMB should ensure that CMS, FBI, IRS, and SSA are collaborating on their cybersecurity requirements pertaining to state agencies to the greatest extent possible and direct further coordination where needed. 

    Agency Affected: Executive Office of the President: Office of Management and Budget

  2. Recommendation: The Director of OMB should take steps to ensure that CMS, FBI, IRS, and SSA coordinate, where feasible, on assessments of state agencies' cybersecurity, which may include steps such as leveraging other agencies' security assessments or conducting assessments jointly. 

    Agency Affected: Executive Office of the President: Office of Management and Budget

  3. Recommendation: The Administrator of CMS should, in collaboration with OMB, solicit input from FBI, IRS, SSA, and state agency stakeholders on revisions to its security policy to ensure that cybersecurity requirements for state agencies are consistent with other federal agencies and NIST guidance to the greatest extent possible and document CMS's rationale for maintaining any requirements variances.

    Agency Affected: Department of Health and Human Services: Centers for Medicare and Medicaid Services

  4. Recommendation: The Administrator of CMS should revise its assessment policies to maximize coordination with other federal agencies to the greatest extent practicable. 

    Agency Affected: Department of Health and Human Services: Centers for Medicare and Medicaid Services

  5. Recommendation: The FBI Director should, in collaboration with OMB, solicit input from CMS, IRS, SSA, and state agency stakeholders on revisions to its security policy to ensure that cybersecurity requirements for state agencies are consistent with other federal agencies and NIST guidance to the greatest extent possible. 

    Agency Affected: Department of Justice: Federal Bureau of Investigation

  6. Recommendation: The FBI Director should fully develop policies for coordinating with state agencies on the use of prior findings from relevant cybersecurity assessments conducted by other organizations. 

    Agency Affected: Department of Justice: Federal Bureau of Investigation

  7. Recommendation: The FBI Director should revise its assessment policies to maximize coordination with other federal agencies to the greatest extent practicable. 

    Agency Affected: Department of Justice: Federal Bureau of Investigation

  8. Recommendation: The IRS Commissioner should, in collaboration with OMB, solicit input from CMS, FBI, SSA, and state agency stakeholders on revisions to its security policy to ensure that cybersecurity requirements for state agencies are consistent with other federal agencies and NIST guidance to the greatest extent possible. 

    Agency Affected: Department of the Treasury: Internal Revenue Service

  9. Recommendation: The IRS Commissioner should revise its assessment policies to maximize coordination with other federal agencies to the greatest extent practicable. 

    Agency Affected: Department of the Treasury: Internal Revenue Service

  10. Recommendation: The Commissioner of SSA should, in collaboration with OMB, solicit input from CMS, FBI, IRS, and state agency stakeholders on revisions to its security policy to ensure that cybersecurity requirements for state agencies are consistent with other federal agencies and NIST guidance to the greatest extent possible and document the SSA's rationale for maintaining any requirements variances. 

    Agency Affected: Social Security Administration

  11. Recommendation: The Commissioner of SSA should fully develop policies for coordinating with state agencies on the use of prior findings from relevant cybersecurity assessments conducted by other organizations. 

    Agency Affected: Social Security Administration

  12. Recommendation: The Commissioner of SSA should revise its assessment policies to maximize coordination with other federal agencies to the greatest extent practicable.

KEYWORDS: Chief Information Security Officer (CISO) cyber security Federal agencies NIST

Share This Story

Looking for a reprint of this article?
From high-res PDFs to custom plaques, order your copy today!
Recommended Content

JOIN TODAY
To unlock your recommendations.

Already have an account? Sign In

  • Cyber tech background

    Security’s Top Cybersecurity Leaders 2026

    Security magazine’s Top Cybersecurity Leaders 2026 award...
    Cybersecurity
  • Iintegration and use of emerging tools

    Future Proof Your Security Career with AI Skills

    AI’s evolution demands security leaders master...
    Career Intelligence
    By: Jerry J. Brennan and Joanne R. Pollock
  • The 2025 Security Benchmark Report

    The 2025 Security Benchmark Report

    The 2025 Security Benchmark Report surveys enterprise...
    The Security Benchmark Report
    By: Rachelle Blair-Frasier
Manage My Account
  • Security Newsletter
  • eMagazine Subscriptions
  • Manage My Preferences
  • Online Registration
  • Mobile App
  • Subscription Customer Service

More Videos

Sponsored Content

Sponsored Content is a special paid section where industry companies provide high quality, objective, non-commercial content around topics of interest to the Security audience. All Sponsored Content is supplied by the advertising company and any opinions expressed in this article are those of the author and not necessarily reflect the views of Security or its parent company, BNP Media. Interested in participating in our Sponsored Content section? Contact your local rep!

close
  • Northland Controls sponsored content
    Sponsored byNorthland Controls

    The Execution Gap: Why Great Security Design Doesn't Always Deliver Great Security

Popular Stories

Man in suit looking out window at city

Why GSOCs and Protective Intelligence Are the Cornerstone of Executive Protection

Photograph of apartment complex patios

Enhancing Residential Building Security

5 Minutes with Johnson

Can Organizations Trust Their Own AI?

Open filing cabinet

The Inside Job: Corporate Espionage Never Went Away

Person working on laptop

When Cyber Meets Physical: Rethinking Data Management for a New Threat Landscape

Events

September 10, 2026

So, You Have an Emergency Management Plan… Now What?

LIVE: September 10, 2026 at 2 PM EDT Turning an emergency management plan into an actionable program that prepares staff, students, and partners to respond effectively is a challenge. Learn to move beyond compliance and build a resilient school safety program.
September 22, 2026

How to Detect, Verify, and Respond to AI-Driven Disinformation

LIVE: September 22, 2026 at 2 PM EDT Identify emerging threats, validate information with confidence, and coordinate an effective response across your organization. Learn how to build the people, processes, and technology needed to improve speed-to-truth.

View All Submit An Event

Products

Security Culture: A How-to Guide for Improving Security Culture and Dealing with People Risk in Your Organisation

Security Culture: A How-to Guide for Improving Security Culture and Dealing with People Risk in Your Organisation

See More Products

Related Articles

  • attack-cyberenews

    GAO: DHS and selected agencies need to address cybersecurity shortcomings

    See More
  • New Executive Order Changes Cybersecurity Requirements for Federal Agencies

    See More
  • Federal Agencies Lagging on FISMA Compliance

    See More

Related Products

See More Products
  • 9780367221942.jpg

    From Visual Surveillance to Internet of Things: Technology and Applications

  • Security of Information and Communication Networks

  • into to sec.jpg

    Introduction to Security, 10th Edition

See More Products

Events

View AllSubmit An Event
  • November 5, 2026

    Ready, Set, Fund: Everything You Need to Know about Winning a Grant and More

    LIVE: November 5, 2026 at 2 PM EDT Discover a dependable process for navigating the competitive funding landscape. Learn how to identify the right opportunities, craft a compelling narrative, and align your goals with grantor expectations. 
View AllSubmit An Event
×

Sign-up to receive top management & result-driven techniques in the industry.

Join over 20,000+ industry leaders who receive our premium content.

SIGN UP TODAY!
  • RESOURCES
    • Advertise
    • Contact Us
    • Store
    • Want More
  • SIGN UP TODAY
    • Create Account
    • eMagazine
    • Newsletter
    • Customer Service
    • Manage Preferences
  • SERVICES
    • Marketing Services
    • Reprints
    • Market Research
    • List Rental
    • Survey/Respondent Access
  • STAY CONNECTED
    • LinkedIn
    • Facebook
    • YouTube
    • X (Twitter)
  • PRIVACY
    • PRIVACY POLICY
    • TERMS & CONDITIONS
    • DO NOT SELL MY PERSONAL INFORMATION
    • PRIVACY REQUEST
    • ACCESSIBILITY

Copyright ©2026. All Rights Reserved BNP Media, Inc. and BNP Media II, LLC.

Design, CMS, Hosting & Web Development :: ePublishing