Extension will allow the Task Force to continue its work as outlined in its recently released Year 2 Report and position itself to support the supply chain risk management imperative in 2021
The Cybersecurity and Infrastructure Security Agency (CISA) announced a six-month extension of the Information and Communications Technology (ICT) Supply Chain Risk Management Task Force. The Task Force, chaired by CISA and the Information Technology (IT) and Communications Sector Coordinating Councils, is a public-private partnership composed of a diverse range of representatives from large and small private sector organizations charged with identifying challenges and devising workable solutions and recommendations for managing risks to the global ICT supply chain.
Biometric security solutions and AI-powered fraud prevention technologies have, for several years now, been transforming the ways in which organizations protect their business, their customers, and their employees. In fact, some industry estimates reveal that AI and biometrics have combined to prevent billions of dollars in losses from fraud—already.
Precisely announced the appointment of Sue Bergamo as Chief Information Security Officer (CISO). In the newly created CISO role at Precisely, she will be responsible for carrying out and managing the company’s information security vision, strategy, and program to minimize potential security risks and further a culture of security stewardship.
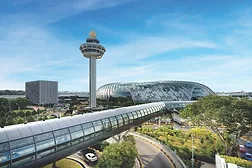
Singapore’s Changi Airport Group, one of the most innovative and technologically advanced airports in the world, will be upgrading and enhancing its security system.
While COVID-19 has slowed the hospitality industry, security plays a more pivotal role than ever and the ongoing pandemic is challenging security professionals to adjust and adapt to new rules and procedures.
While COVID-19 has slowed the hospitality industry, security plays a more pivotal role than ever and the ongoing pandemic is challenging security professionals to adjust and adapt to new rules and procedures. And yet, as the pandemic and challenging economy continues, security departments within the hospitality industry are increasingly tasked to do more with less.
While many organizations understand the need for a security executive, organizations that have taken a holistic approach, have added the chief risk officer (CRO) position to evaluate all organizational risk. So, what is a chief risk officer, who makes a good candidate, where does the CRO stand organizationally within an enterprise, and what value does one add? Here are all your CRO questions answered.
McKinsey & Company reports that most risk managers at large organizations are flying blind when it comes to evaluating their cyber resilience due to bloated reporting processes and overly complicated reporting tools. Here's how organizations can implement a risk-based approach to their cybersecurity controls.
The modern workplace will likely remain partially remote long term, so a robust remote cybersecurity program is now a critical element of your cybersecurity program, which may require a larger IT staff or assistance from a managed IT provider.
The daunting threats and attack techniques from 2020 are expected to continue into this year. And while 2021 offers a fresh start, cybercriminals will continue to become increasingly savvy, deploying a wide range of techniques to extort, disrupt, and infiltrate organizations. Now more than ever, government and corporate leaders and consumers must become engaged in ensuring effective cybersecurity strategies are in place. Here are eight steps organizations can implement to heighten cybersecurity governance:
Despite the heavy reliance on the 20-year-old technology, Active Directory, cybersecurity efforts seem to continuously overlook this obvious and frequent target, which only puts organizations at further risk. Despite cybersecurity advances, Active Directory is still one part of an organization’s environment that gets the least cybersecurity attention. While most security programs have a SIEM solution monitoring logs for anything out of the norm, this is simply not enough.