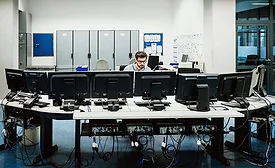
Like many other industry buzzwords, there’s a lot of hype around security automation. Yet, for the first line of defense in an enterprise environment, the analysts working in the security operations center (SOC), the notion of automation is more headline than reality. Many basic tasks – logging, fault isolation, reporting, and incident troubleshooting – are still very much manual.
The new Panda Security Threat Insights Report 2020 compiled by PandaLabs – anti-malware laboratory and security operations center (SOC) –illuminates several emerging trends in the cybersecurity space.
Mimecast Limited released the latest report from the Cyber Resilience Think Tank highlighting four trends for building and operating a Security Operating Center (SOC).
The Cybersecurity and Infrastructure Security Agency (CISA) has released a guide, Critical Infrastructure Operations Centers and Control Rooms Guide for Pandemic Response, geared towards all 16 critical infrastructure sectors.
“For many people who work in enterprise security, there’s no straight line to get there. That was my situation, too,” says Jerry Loghry, AVP Corporate Security & Safety for EMC Insurance Companies.
Enterprises are struggling to find the right talent to safeguard their networks; therefore, they must change their mindsets and begin recruiting talent from non-traditional backgrounds to ensure they have the "right" person on their SOC team.
More than 10 years ago, I was deployed to Iraq as a U.S. Air Force intelligence analyst, assigned to the Joint Special Operations Command (JSOC) Task Force with one clear objective: disrupt terrorist activities by targeting and capturing al-Qaeda insurgents.
More than half of organizations (53 percent) rate their Security Operation Center’s (SOC) ability to gather evidence, investigate and find the source of threats as ineffective, according to the Improving the Effectiveness of the Security Operations Center study.