Security Magazine logo
search
cart
facebook twitter linkedin youtube
  • Sign In
  • Create Account
  • Sign Out
  • My Account
Security Magazine logo
  • NEWS
    • Security Newswire
    • Technologies & Solutions
  • MANAGEMENT
    • Leadership Management
    • Enterprise Services
    • Security Education & Training
    • Logical Security
    • Security & Business Resilience
    • Profiles in Excellence
  • PHYSICAL
    • Access Management
    • Fire & Life Safety
    • Identity Management
    • Physical Security
    • Video Surveillance
    • Case Studies (Physical)
  • CYBER
    • Cybersecurity News
    • More
  • BLOG
  • COLUMNS
    • Career Intelligence
    • Cyber Tactics
    • Cybersecurity Education & Training
    • Leadership & Management
    • Security Talk
  • EXCLUSIVES
    • Annual Guarding Report
    • Most Influential People in Security
    • The Security Benchmark Report
    • Top Guard and Security Officer Companies
    • Top Cybersecurity Leaders
    • Women in Security
  • SECTORS
    • Arenas / Stadiums / Leagues / Entertainment
    • Banking/Finance/Insurance
    • Construction, Real Estate, Property Management
    • Education: K-12
    • Education: University
    • Government: Federal, State and Local
    • Hospitality & Casinos
    • Hospitals & Medical Centers
    • Infrastructure:Electric,Gas & Water
    • Ports: Sea, Land, & Air
    • Retail/Restaurants/Convenience
    • Transportation/Logistics/Supply Chain/Distribution/ Warehousing
  • EVENTS
    • Industry Events
    • Webinars
    • Solutions by Sector
    • Security 500 Conference
  • MEDIA
    • Interactive Spotlight
    • Photo Galleries
    • Podcasts
    • Polls
    • Videos
      • Cybersecurity & Geopolitical Discussion
      • Ask Me Anything (AMA) Series
  • MORE
    • Call for Entries
    • Classifieds & Job Listings
    • Newsletter
    • Sponsor Insights
    • Store
    • White Papers
  • EMAG
    • eMagazine
    • This Month's Content
    • Advertise
  • SIGN UP!
CybersecuritySecurity NewswireCybersecurity News

PHP Issues Patches for Two Critical Flaws, Security Leaders Discuss
By Jordyn Alger, Managing Editor
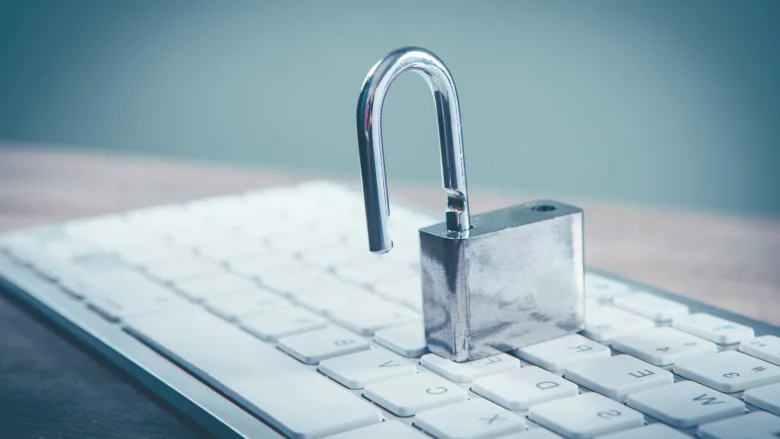
Open padlock on keyboard
Sasun Bughdaryan via Unsplash
October 22, 2026

PHP, which is used in most major operating systems, has issued fixes for two critical vulnerabilities. Given the widespread nature of PHP, the vulnerabilities can lead to highly-exploitable environments, and so organizations are urged to patch these flaws immediately — especially since they can enable unauthenticated remote code execution. 

Ben Ronallo, Principal Cybersecurity Engineer at Black Duck, warns, “This is a genuine drop-everything moment for anyone running PHP. The flaws are in the PHP engine itself, so a perfectly secure application on top of a vulnerable runtime is still exposed. Updating WordPress or your framework won’t fix it. You must update PHP itself and restart the services that run it.

“It’s understandable that people are confused about how this unfolded. Word of the vulnerabilities leaked on Y Combinator’s Hacker News forum two days before the planned disclosure, and PHP moved its security release up a day in response. The source of the leak hasn’t been identified, but there’s no evidence a threat group was involved, and no exploit code was released. A screenshot of the researchers’ exploit tool did circulate, which added to the alarm. In the end, the early reports were largely accurate. The main difference is severity: PHP officially rates both flaws 9.2 rather than the 10.0 some reports cited. That’s still critical, and it doesn’t change the advice.

“The organizations I’m most concerned about are the ones that don’t know where PHP is running in their environment. Older versions sitting in containers, appliances, or legacy sites won’t receive an official fix. Nobody wants to be building a software inventory in the middle of an emergency. You need that visibility before the next one hits.”

Tim Mackey, Head of Software Supply Chain Risk Strategy at Black Duck, adds, “Preventing leaks of any vulnerability data for a CVE prior to an embargo for the patch being published is precisely what coordinated vulnerability disclosure processes are designed to protect against. When a leak, or advance knowledge, of a vulnerability occurs the entire ecosystem surrounding the vulnerability is placed at risk. As details of the leak are published, security defenders are faced with the real risk that malicious actors could use the absence of an official patch to supply their own malicious patches. 

“Defenders should pay extra attention to the origin of their patches and validate functional changes against official release notes. After all, a malicious patch could implant a backdoor for future use and a rush to patch might present the right opportunity for malicious actors.”

KEYWORDS: vulnerability vulnerability assessment vulnerability management

Share This Story

Looking for a reprint of this article?
From high-res PDFs to custom plaques, order your copy today!

Jordynalger

Jordyn Alger is the managing editor for Security magazine. Alger writes for topics such as physical security and cyber security and publishes online news stories about leaders in the security industry. She is also responsible for multimedia content and social media posts. Alger graduated in 2021 with a BA in English – Specialization in Writing from the University of Michigan. Image courtesy of Alger

Recommended Content

JOIN TODAY
To unlock your recommendations.

Already have an account? Sign In

  • Cyber tech background

    Security’s Top Cybersecurity Leaders 2026

    Security magazine’s Top Cybersecurity Leaders 2026 award...
    Cybersecurity
  • Iintegration and use of emerging tools

    Future Proof Your Security Career with AI Skills

    AI’s evolution demands security leaders master...
    Career Intelligence
    By: Jerry J. Brennan and Joanne R. Pollock
  • The 2025 Security Benchmark Report

    The 2025 Security Benchmark Report

    The 2025 Security Benchmark Report surveys enterprise...
    The Security Benchmark Report
    By: Rachelle Blair-Frasier
Manage My Account
  • Security Newsletter
  • eMagazine Subscriptions
  • Manage My Preferences
  • Online Registration
  • Mobile App
  • Subscription Customer Service

More Videos

Sponsored Content

Sponsored Content is a special paid section where industry companies provide high quality, objective, non-commercial content around topics of interest to the Security audience. All Sponsored Content is supplied by the advertising company and any opinions expressed in this article are those of the author and not necessarily reflect the views of Security or its parent company, BNP Media. Interested in participating in our Sponsored Content section? Contact your local rep!

close
  • Northland Controls sponsored content
    Sponsored byNorthland Controls

    The Execution Gap: Why Great Security Design Doesn't Always Deliver Great Security

Popular Stories

Laptop with green code

FBI Removes Accenture Contractor Following Employee Data Breach

McDonald's

40M McDonald's Records Exposed Through Customer Data Platform

3D map

Why Location Intelligence is Becoming Critical for Emergency Response and Security Operations

Man in suit looking out window at city

Does Your CISO Have the Authority the Job Now Requires?

School hallway

Frontline Education Data Breach Highlights Third-Party Risks


AlertMedia sponsored webinar

Events

October 28, 2026

From Alert to Evidence: 5 Steps to Faster Endpoint Investigations

LIVE: October 28, 2026 at 2 PM EDT Attendees will learn how to reduce repetitive manual work, identify affected users and systems sooner, and communicate findings that security, legal, compliance, and executive stakeholders can review and verify.

October 29, 2026

2026 Active Assailant Preparedness Benchmarks: How Ready Is Your Organization?

LIVE: October 29, 2026 at 2 PM EDT When an active assailant incident unfolds, teams need to make decisions with clear, timely information. How ready are organizations? We'll discuss the 2026 Everbridge research on active assailant preparedness.

View All Submit An Event

Products

Security Culture: A How-to Guide for Improving Security Culture and Dealing with People Risk in Your Organisation

Security Culture: A How-to Guide for Improving Security Culture and Dealing with People Risk in Your Organisation

See More Products

Related Articles

  • Hamburger

    Security Leaders Discuss Restaurant Brands International’s Vulnerabilities

    See More
  • Red and black technological patterns

    5 ICS advisories released by CISA, security leaders discuss

    See More
  • Pink neon lights

    Warning issued for 10-year-old vulnerability, security leaders discuss

    See More

Related Products

See More Products
  • Photonic Sensing: Principles and Applications for Safety and Security Monitoring

See More Products

Events

View AllSubmit An Event
  • July 8, 2026

    The 2026 Security Maturity Benchmark Report: Insights From Senior Security Leaders

    ON DEMAND: In this webinar, speakers will share key insights from the 2026 Security Maturity Benchmark Report, including why today’s threat environment demands greater maturity and how to evaluate your organization’s current security posture.
View AllSubmit An Event
×

Sign-up to receive top management & result-driven techniques in the industry.

Join over 20,000+ industry leaders who receive our premium content.

SIGN UP TODAY!
  • RESOURCES
    • Advertise
    • Contact Us
    • Store
    • Want More
  • SIGN UP TODAY
    • Create Account
    • eMagazine
    • Newsletter
    • Customer Service
    • Manage Preferences
  • SERVICES
    • Marketing Services
    • Reprints
    • Market Research
    • List Rental
    • Survey/Respondent Access
  • STAY CONNECTED
    • LinkedIn
    • Facebook
    • YouTube
    • X (Twitter)
  • PRIVACY
    • PRIVACY POLICY
    • TERMS & CONDITIONS
    • DO NOT SELL MY PERSONAL INFORMATION
    • PRIVACY REQUEST
    • ACCESSIBILITY

Copyright ©2026. All Rights Reserved BNP Media, Inc. and BNP Media II, LLC.

Design, CMS, Hosting & Web Development :: ePublishing