The Cybersecurity and Infrastructure Security Agency (CISA) recently published an alert on the Dridex malware, as the result of recent collaboration between the Department of the Treasury Financial Sector Cyber Information Group (CIG) and the Department of the Treasury’s Financial Crimes Enforcement Network (FinCEN) to identify and share information with the financial services sector.
The U.S. State Department, in partnership with the FBI, announced a reward of up to $5 million under the Transnational Organized Crime Rewards Program for information leading to the arrest and/or conviction of Russian nationals accused of serious cyber crimes.
Clark Atlanta University (CAU) and Augusta University (AU) have forged a partnership between the CAU Department of Cyber-Physical Systems and the School of Computer and Cyber Sciences at Augusta University.
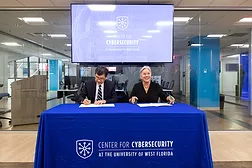
The University of West Florida and the Jikei College Group in Japan announced a partnership that aims to enhance global cybersecurity workforce development.
Differences in cultural values have led some countries to tackle cyber attacks with increased internet regulation, while others have taken a ‘hands-off’ approach to online security.
What is a Defense-in-Depth strategy, and why has it come to be acknowledged as Expense-in-Depth? How can CISO's communicate the business value of this strategy?
The Cybersecurity and Infrastructure Security Agency (CISA) issued a draft binding operational directive, BOD 20-01, which will require federal civilian executive branch agencies to publish a vulnerability disclosure policy (VDP).